Secure Webhook Intake System with HMAC Verification
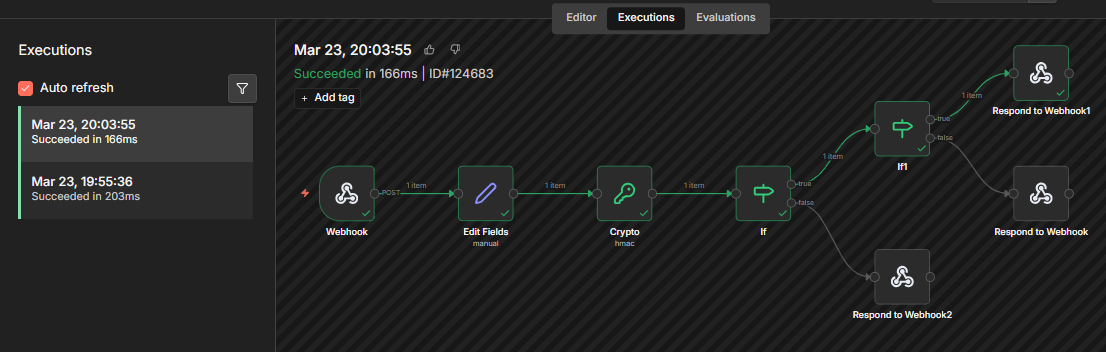
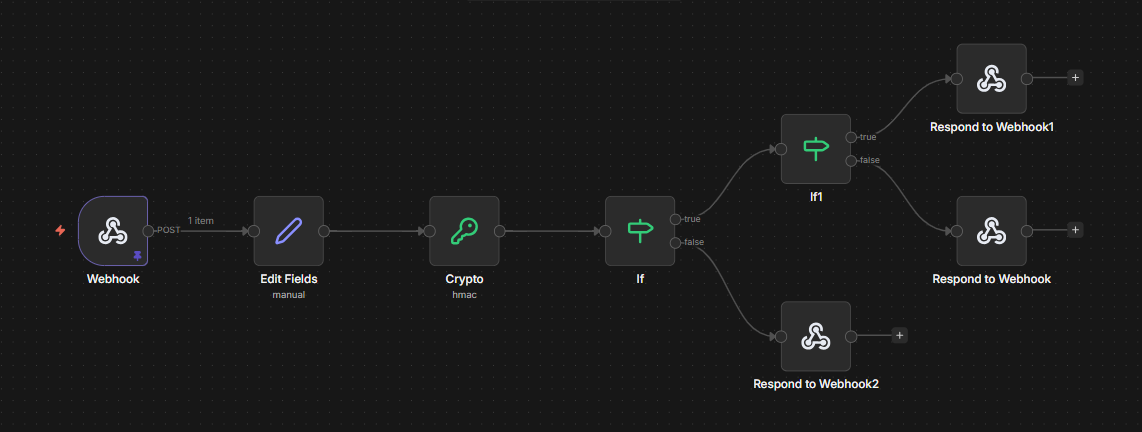
A production-grade n8n workflow that validates inbound webhook events before accepting them: header auth blocks unknown callers, HMAC signature verification confirms payload integrity, and timestamp validation prevents replay attacks.
The Problem
Security firms and SOC teams receive events from external sources: SIEMs, threat feeds, ticketing systems, and custom scripts. Without a verified intake gate, any caller can push malicious or spoofed data into your automation pipeline.
Manual verification is not scalable. One misconfigured endpoint is all it takes.
The Solution
A layered webhook intake system with three enforcement points:
- Header Auth blocks any request without the pre-shared API key
- HMAC-SHA256 signature check verifies the payload was signed by
- Timestamp window (plus/minus 5 minutes) eliminates replay attacks
Use Cases
- Inbound event intake for MDR alert pipelines
- Verified webhook receivers for GRC compliance triggers
- Secure API gateway layer for SOC-as-a-Service platforms
- Threat intel feed ingestion with integrity enforcement
Impact
Eliminates blind webhook trust. Adds cryptographic verification and replay protection to any inbound automation endpoint without custom code or external services.
Built by Kunsh Tanwar | [email protected]